Identifying cyber threats is an important part of the cybersecurity risk management process. Cyber threats include things like malware, which is harmful software; phishing, which tricks people into giving away personal information; ransomware, which locks your files until you pay money; and denial-of-service (DoS) attacks, which overload a system to make it unavailable. To protect against these threats, organizations need to be alert and regularly check their systems and networks. Using threat intelligence can help you spot dangers early and take action to stop them. By including regular monitoring and threat intelligence in your cybersecurity risk management process, you can defend your business better against new risks.
Assessing vulnerabilities is another critical step in identifying potential cyber risks. Vulnerabilities can arise from various sources, including software and hardware flaws, misconfigured systems, and human error. Regular vulnerability assessments help organizations identify these weaknesses and prioritize remediation efforts. By conducting thorough assessments, you can uncover your hidden vulnerabilities that could be exploited by cyber threats. This proactive approach to managing cyber risks ensures that you can address potential issues before they lead to significant security breaches.
Without proper risk management, businesses leave themselves exposed to costly and disruptive cybersecurity incidents, such as:
According to a recent report, 46% of cyberattacks target small businesses, yet many owners believe they’re too small to be a target. Implementing cybersecurity risk management helps you:
A successful risk management program follows three core principles:
Let’s break these down further.
A risk analysis involves risk identification to understand how exposed your business is to potential threats and vulnerabilities. For example:
Say your business uses a cloud platform to store sensitive client data, a risk analysis may identify weak password policies or lack of multi-factor authentication (MFA) as vulnerabilities.
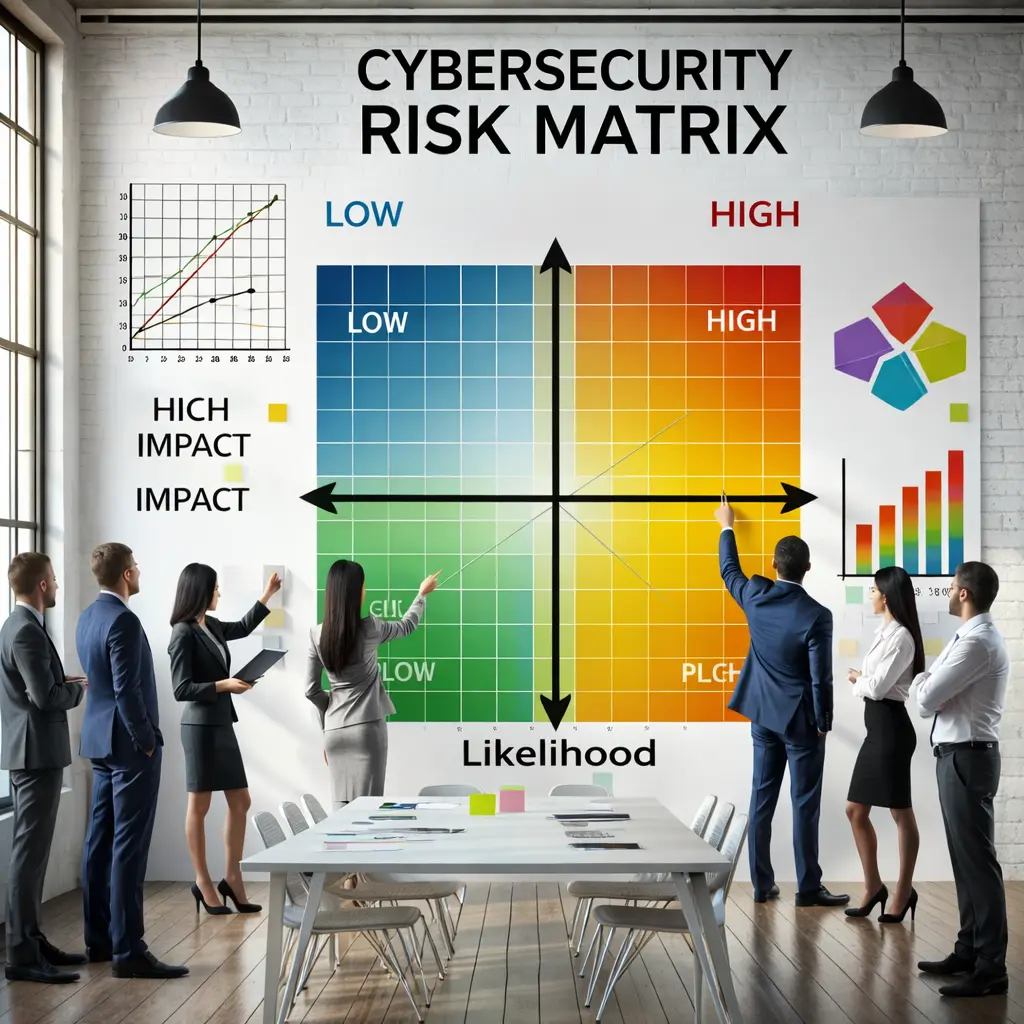
Once you’ve identified risks, a risk assessment evaluates their potential impact and likelihood. It categorizes risks based on severity, helping you prioritize which ones to address first.
Effective risk management processes involve continuous assessment and review to keep pace with evolving threats.
Key Questions to Ask During a Thorough Risk Assessment:
For example, a small retail business may determine that losing customer payment data to a hacker would have a high impact and likelihood without proper encryption. Therefore, this risk becomes a top priority.
Find out where your vulnerabilities are with our 15 Minute Risk Assessment: Click Here to Access
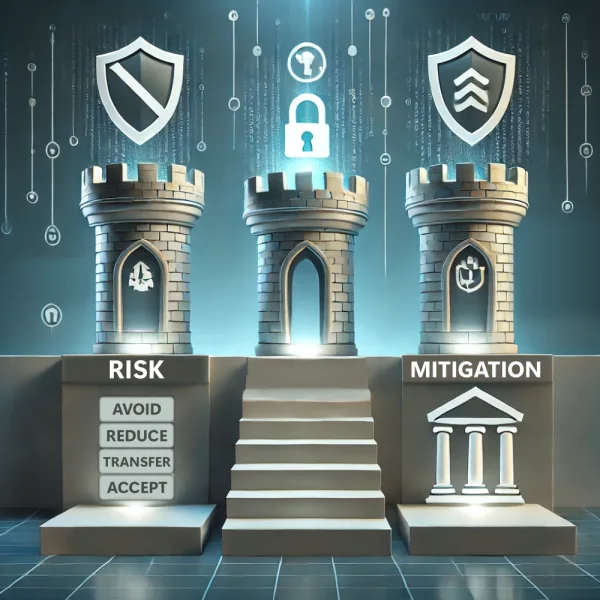
Once risks are analyzed and assessed, managing risk involves applying on or more of the following strategies to reduce them.
The four main strategies are:
1. Avoid
If a risk is too great and not worth taking, avoid it all together.
Example: Starting an online store without a secure payment gateway is too risky. Avoid launching until proper security measures are in place.
2. Reduce (Minimize)
Reducing risk means taking steps to lower the likelihood or impact of a threat.
Example: Implementing a firewall, regular software updates, and employee security training reduces the risk of malware and phishing attacks.
3. Transfer
Transfer risk by outsourcing certain responsibilities or purchasing cybersecurity insurance.
Pro Tip: Before purchasing cyber insurance, conduct a Cyber Insurance Readiness Assessment to ensure you understand coverage needs.
4. Accept
Some risks are low impact and don’t justify expensive mitigation. In such cases, businesses may choose to accept the risk.
Example: A small office network may decide that the minimal risk of printer misuse isn’t worth implementing advanced controls.
Note: Always document accepted risks and make sure leadership approves them to avoid surprises later.
Not all risks are equal. Use a risk matrix to prioritize risks based on impact and likelihood.
Use multiple layers of defense to reduce vulnerabilities. Examples include:
Human error is one of the top causes of cybersecurity incidents. Educating your employees can significantly lower risks.
Cyber threats evolve constantly, so your risk management program must adapt:
Every organization needs a solid cybersecurity framework in order to manage risks. A structured cybersecurity framework provides a comprehensive approach to addressing all aspects of cybersecurity, including risk management, threat intelligence, incident response, and continuous monitoring. Organizations can leverage established frameworks, such as NIST or ISO 27001, to build their cybersecurity framework. These frameworks offer best practices that help organizations create a robust and resilient cybersecurity posture.
60% of small businesses close within six months of a cyberattack. Ignoring cybersecurity risk management can have severe consequences:
Implementing a cyber risk management initiative can help businesses prioritize and handle critical threats in a timely manner.
Don’t let this happen to your business – proactive risk management is the key to long-term success.