A large post-secondary institution faced exposure in their cybersecurity protection measures and required urgent remediation and long term management planning.
What was needed:
· Creation of policy and management planning to bring them into alignment with cybersecurity industry best practices and regulatory compliance
· Risk reduction strategies that could be implemented immediately
The institution has an effective IT department but lacked senior staff with enterprise-level security experience, and they did not have staffing budget to hire additional senior positions.
As a higher education institution with tens of thousands of students, faculty, contractors, suppliers and staff, the institution was at a high exposure to phishing, ransomware, loss of credentials, and other malware attacks.
Gaining a clear understanding of the problem and writing a carefully constructed security management plan will result in a resource that will pay back future benefits.
The organization needed an evaluation of their current security position and risk profile.
We needed to establish a cybersecurity and cyber risk management program, as well as bring the IT team to a level of maturity. This required defining the scope and terms of reference for the team.
First, we defined a ransomware attack and disaster response plan. Then we introduced management reporting to show current status.
To provide confidence to management we included regular auditing of cybersecurity readiness with reports to show ongoing effectiveness needed to be established.
We prepared a cybersecurity advisory service report and a Risk Assessment to identify the threats and their importance.
We created a risk register of the existing IT and security landscape to prioritize remediation steps.
We worked together with the information technology departments staff and management to review their current IT environment and build a plan to bring the college into alignment with cybersecurity industry best practices and compliance with recognized frameworks and standards.
Next, we created an action plan to address high priority security and infrastructure issues.
We also built a long-term strategic and tactical management plan to bring the cybersecurity team to the target state of maturity within the resources that were available.
Together with IT Department management, we established a Cybersecurity Team (CST) within the IT department, including assisting with creation of job descriptions, assessing candidates for employees, assigning responsibilities and providing professional input in the selection process.
We developed an organizational framework and Terms of Reference that would leverage the new CST security resources.
Developed management reporting that is used to inform the executive staff and audit committee of the status of the CST and the roadmap to get the organization to a position of accountability, safety and compliance.
Created reports to document the steps taken, which are essential to meet industry standards and compliance with regulations.
We met in person with the stakeholder team and managers to present solution options for acceptance.
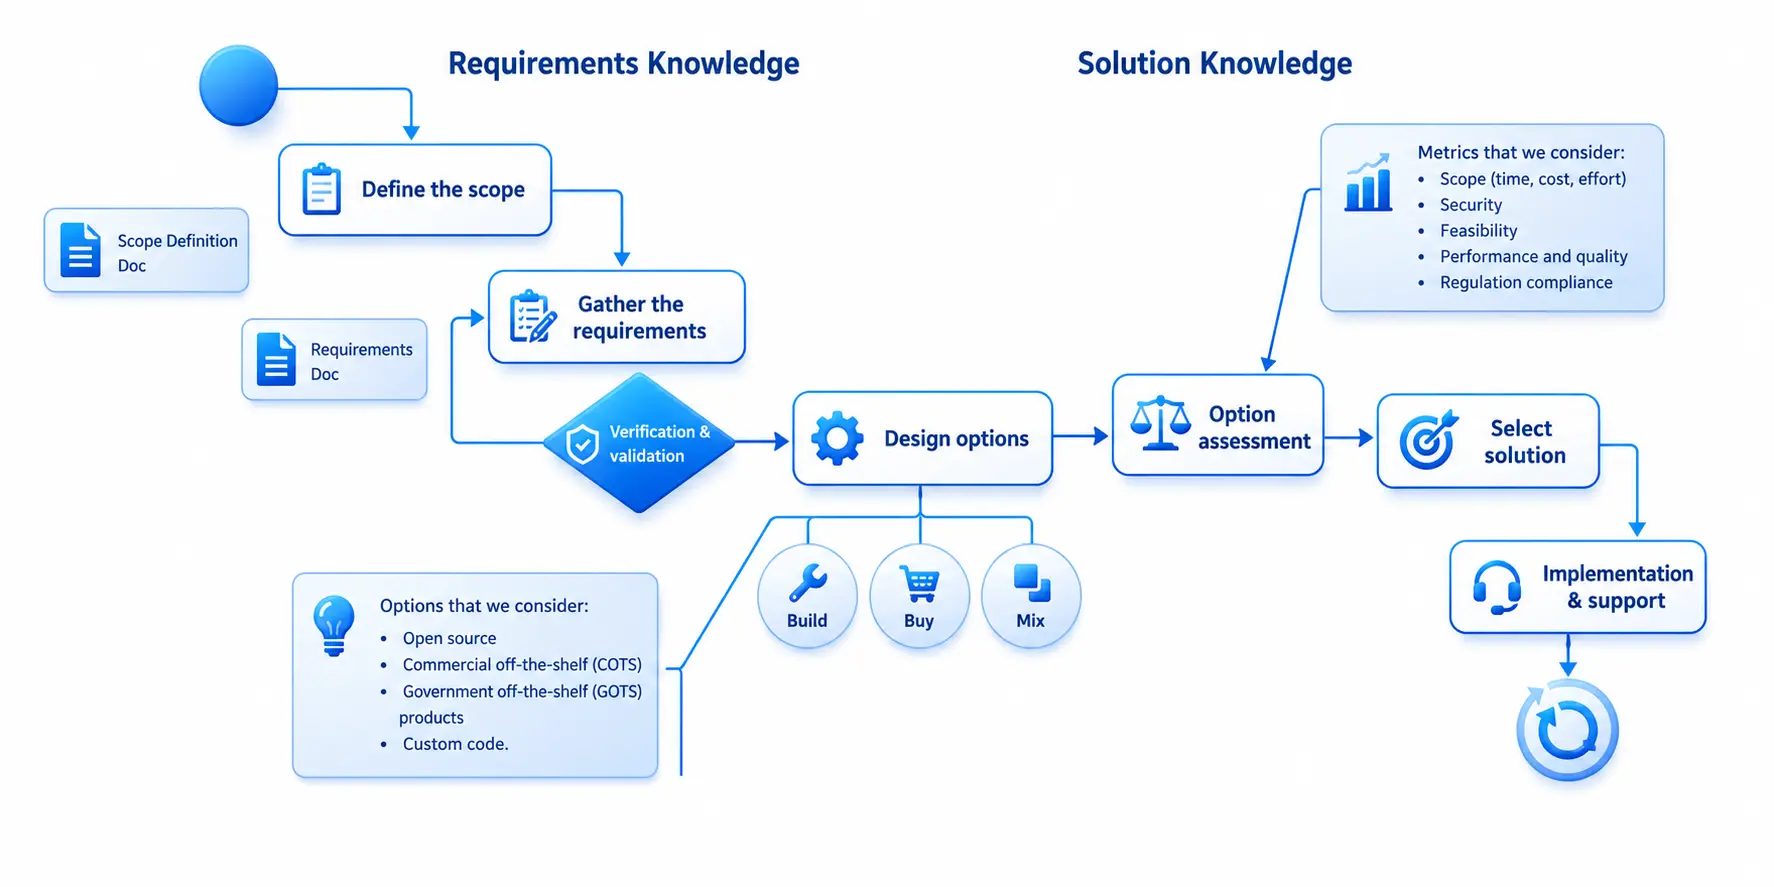
The institution is now at a much more protected level in day-to-day operation.
Reporting is in place to show compliance with requirements and industry-standard practices.
They now have a functional group within the IT department with the framework, policies and plans to maintain the systems and protection. The CST has defined duties, plus the ownership and authority to act in-house on existing and expected threats.
They benefit from a secure foundation to build on for additional levels of IT/security maturity and meeting standards.
Lighthouse provides continuing executive-level advice and guidance to the CIO and senior staff on strategy and procedures to protect the institution and assist them in realizing their mission of delivering excellence in education.
The human factor is always the weakest link in the chain. The next point in the plan is building out an e-mail phishing awareness training program, to encourage more people to learn how to act in a security-aware manner within the institution, and out in the world.
Cybersecurity Information for large organizations and infrastructure https://cyber.gc.ca/en/large-organizations-infrastructure
Cybersecurity advice and guidance for universities, colleges, research institutions, school boards and other academic organizations https://cyber.gc.ca/en/academia
NIST Cybersecurity standards https://www.nist.gov/cybersecurity
ISO/IEC 27001 Information Security Management standards https://www.iso.org/standard/27001